Meaning
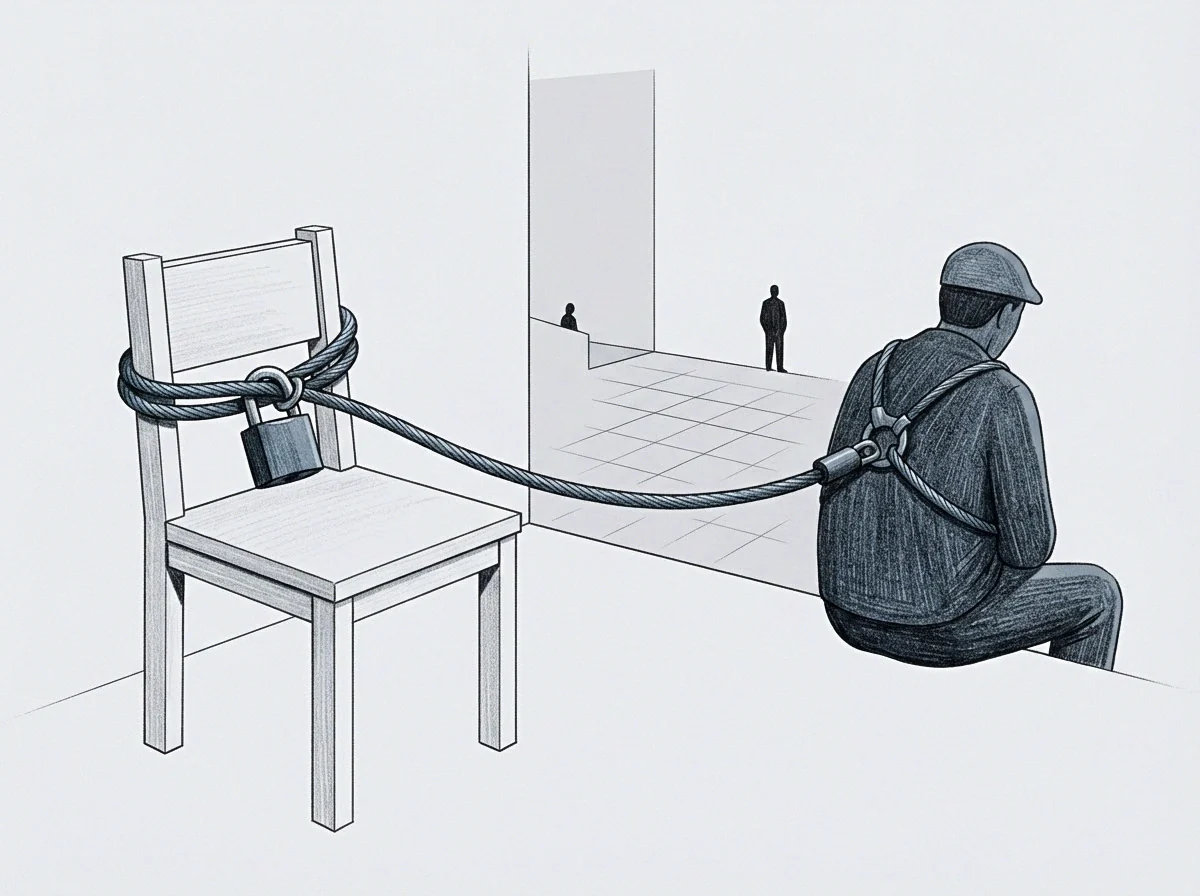
Administrative or technical boundaries define the scope of data or physical resources available to specific roles within an organization. Within an established venture, access limits act as a control mechanism to prevent unauthorized interaction with sensitive infrastructure. These constraints operate on a binary scale of permission or a gradient of visibility depending on the seniority of the observer.
They exist to maintain security protocols and ensure that information flow remains contained within relevant operational silos. By limiting the number of entry points to a database or a physical office, the organization reduces its total attack surface. This containment ensures that a breach in one department does not automatically compromise the entire entity.
Control Mechanism
Security of the network depends on the rigidity of these protocols. When access limits are too broad, the risk of data leakage increases. Conversely, overly restrictive settings prevent teams from obtaining the inputs required for high velocity work.
The trade off involves balancing the speed of execution against the safety of intellectual property.
Systemic Impact
Resource allocation becomes more predictable when barriers are clearly mapped. The presence of access limits allows for a clear audit trail of who touched what asset and when. Such tracking is essential for regulatory filings and internal forensics.
Efficiency gains occur when the boundaries match the actual requirements of the job description.
Resource Alignment
Protocols remain effective only while the underlying identity management system remains accurate. If a user moves to a new department but retains old permissions, the integrity of the perimeter fails. Regular audits of these settings ensure the barrier remains aligned with current organizational charts.